Cisco has published a High rated advisory for the remote access SSL VPN on Cisco Secure Firewall ASA Software, and says it is being exploited. CISA added the same flaw to its Known Exploited Vulnerabilities catalog the next day. If you run an ASA 5500-X with SSL remote access VPN and a second login factor, this one is about you. This post covers what the flaw does, how to tell if a box is exposed, which release fixes it on the models still in the field, and the certificate trust change Cisco has flagged for the same firewalls.
What Cisco published
Cisco's advisory went out on 2026 October 28 as CVE-2026-76418 with a CVSS base score of 8.6. In Cisco's words, the flaw "could allow an unauthenticated, remote attacker to cause the device to reload unexpectedly, resulting in a denial of service (DoS) condition." The cause is narrow: "This vulnerability is due to logic errors when secondary authentication is configured on a tunnel group."
The line that matters most sits near the end of the notice: "In October 2026, the Cisco PSIRT became aware of active exploitation of this vulnerability." For a firewall at the edge of a site, an unexpected reload is an outage for everything behind it.
CISA lists it as exploited
CISA's catalog feed shows the entry with the date added 2026-10-29 and a due date of 2026-11-01 for federal agencies. The required action reads: "Apply mitigations in accordance with vendor instructions". For a private network the catalog is not a rule, but it is a plain signal: this is not a theoretical bug.
Is your ASA exposed?
Cisco lists three conditions, and all three must hold. The box runs "a vulnerable release of Cisco Secure Firewall ASA Software", "the SSL remote access VPN login service is reachable", and "secondary authentication is configured in the tunnel group scope". Here is how to check each one.
- SSL VPN enabled. Cisco's test: "If the running configuration contains the webvpn keyword and SSL VPN is enabled on at least one interface, the configuration is vulnerable".
- Secondary authentication in a tunnel group. With the group list on, Cisco says to "check all tunnel groups, including the default tunnel group, DefaultWEBVPNGroup , for secondary-authentication-server-group". With it off, check the default group anyway, "because disabling the group list does not remove exposure when that default group uses secondary authentication."
- No login needed. Cisco notes: "A successful VPN login is not required to reach the affected processing path."
A firewall that only does site to site IPsec, or that has no second factor set in any tunnel group, does not meet the conditions Cisco lists.
Fixed releases
Cisco says "There are no workarounds that address this vulnerability", and "Cisco strongly recommends upgrading to the fixed software". The ASA table in the advisory:
| ASA release train | First fixed release |
|---|---|
| 9.16 and earlier | 9.16.4.104 |
| 9.18 | 9.18.4.96 |
| 9.20 | 9.20.4.50 |
| 9.22 | 9.22.3.200 |
| 9.23 | 9.23.1.48 |
| 9.24 | 9.24.1.27 or 9.24.10.1 |
What it means for ASA 5500-X owners
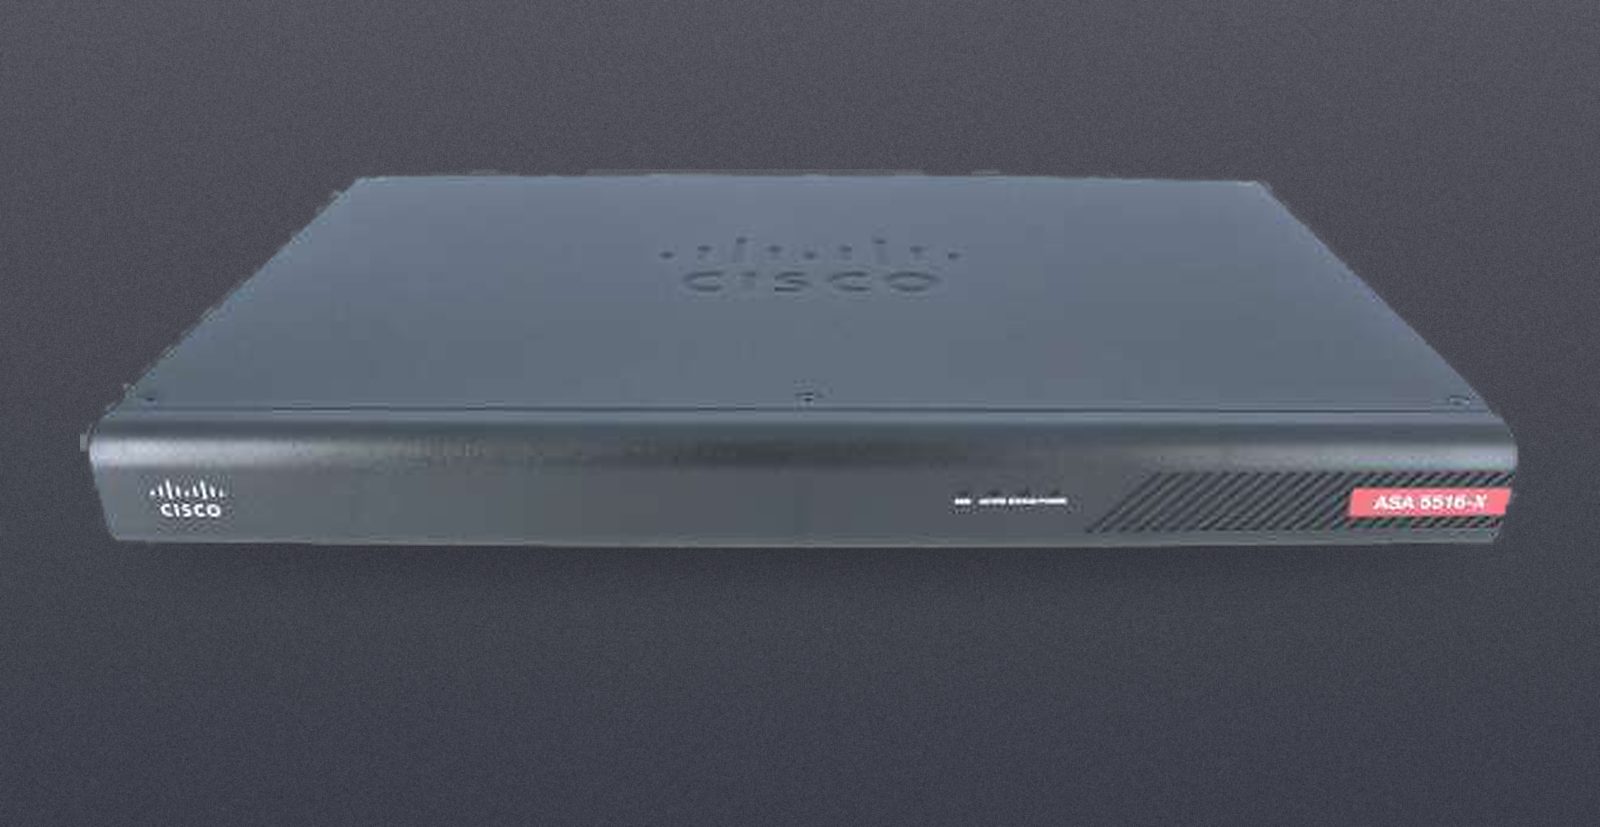
The fixed release you can use depends on the last train your model runs. Cisco's compatibility guide states: "ASA 9.16(x) was the final version for the ASA 5506-X, 5506H-X, 5506W-X, 5508-X, and 5516-X." For a 5508-X or 5516-X, the line that applies in the table is "9.16 and earlier", so the target is 9.16.4.104.
The same guide says: "ASA 9.12(x) was the final version for the ASA 5512-X, 5515-X, 5585-X, and ASASM." The advisory's table names no fix inside the 9.12 train, so on a 5585-X the step the advisory leaves you is its mitigation. Cisco gives two cases. If the default group does not use secondary authentication, turn off the group list: "In WebVPN configuration mode, enter no tunnel-group-list enable ." If it does, remove the second factor with "the no secondary-authentication-server-group CLI command". Cisco is blunt about the cost of the second case: "With secondary authentication disabled, the security posture is lowered for remote access VPN." Treat that as a stopgap while you plan a platform that runs a fixed train.
The certificate trust change on the same boxes
A second Cisco notice touches the same firewalls. The eMudhra informational, last updated 2026 November 4, covers a broken certificate authority: "the private keys for eight eMudhra intermediate certificates were fundamentally broken". Cisco lists "Secure Firewall Adaptive Security Appliance" under "Impacted Products with Remediation Steps" and points to its own firewall guidance page. If your ASA relies on certificates, read that guidance alongside the VPN fix and plan both for one maintenance window.
Buying or keeping one
If you are buying an ASA for remote access VPN, plan the software first. A 5508-X or 5516-X bought today should go into service on the fixed 9.16 build, and a 5585-X should go in only where the mitigation above is acceptable. We have the Cisco ASA 5508-X, the ASA 5516-X and an ASA 5585-X in stock; every ASA we carry is on the ASA shelf, and other firewalls are under security.
Our own read of the market this week: used ASA 5508-X units are listed far more often than new ones, and the 5516-X is the harder of the two to find. If the box has to go into service on a fixed build, say so when you ask for a quote. For what changed when these models left Cisco support, see our earlier post on the ASA 5508-X and 5516-X after end of support, and the Cisco guide for the rest of the line.