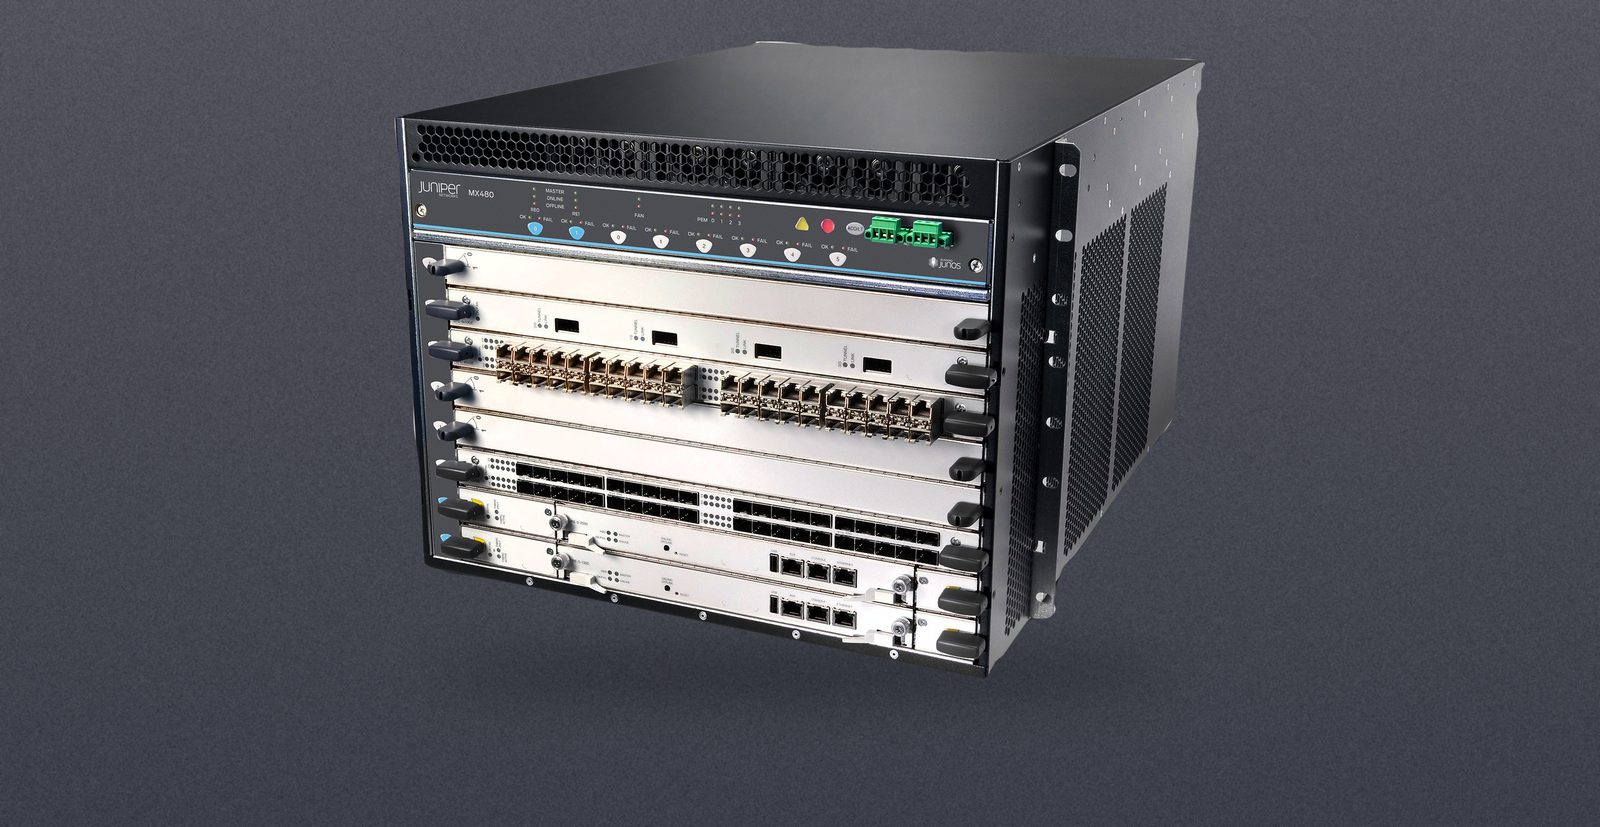
Cisco published a High rated advisory on 2026 October 21 for IOS XR on the ASR 9000 family: crafted IPv4 packets can reset the network processor on certain line cards, and repeated resets can shut a card down until someone reloads it. It does not touch every ASR 9000. Which line cards are installed decides it, and Cisco names them. This post sets out who is exposed, the fixed releases, the stopgap filter Cisco gives, and a second Cisco notice that brings an IOS XR release date for the eMudhra certificate problem.
What Cisco published
The advisory is CVE-2026-76505, base score 7.5. Cisco's summary: a flaw in IPv4 packet processing "could allow an unauthenticated, remote attacker to cause network processor (NP) errors, resulting in a line card reset or shutdown and a denial of service (DoS) condition."
The packets have to be aimed at the router itself. Cisco says the bug is in "crafted IPv4 packets that are received on an affected line card interface and processed as for-us traffic", and that "Transit IPv4 traffic does not trigger this issue and IPv6 traffic cannot trigger it." The damage can outlast the attack: "Under repeated reset conditions, the network processor may enter a persistent shutdown state, in which case an explicit line card reload may be required to restore traffic."
Which routers and line cards
Cisco lists the products when they run "a vulnerable release of Cisco IOS XR 64-bit Software and have IPv4 enabled for any interface on any of the installed line cards":
- "ASR 9000 Series Aggregation Services Routers if they have a Lightspeed- or Lightspeed-Plus-based line card installed"
- "ASR 9900 Series Aggregation Services Routers if they have a Lightspeed- or Lightspeed-Plus-based line card installed"
- "ASR 9902 Compact High-Performance Routers" and "ASR 9903 Compact High-Performance Routers"
The Lightspeed cards Cisco names start with "A9K-16X100GE-TR A99-16X100GE-X-SE A99-32X100GE-TR", and the Lightspeed-Plus list includes "A9K-4HG-FLEX-SE A9K-4HG-FLEX-TR A9K-8HG-FLEX-SE". The full lists are in the advisory. To see what is in your chassis, Cisco says "use the show platform CLI command". Cisco is also clear on the edges: "Only products listed in the Vulnerable Products section of this advisory are known to be affected by this vulnerability."
So for an ASR 9000 chassis, the question is the line cards and the software, not the chassis. A router on IOS XR 64-bit with none of the named cards installed does not meet the conditions Cisco lists.
Fixed releases
| IOS XR release | First fixed release |
|---|---|
| 7.8 and earlier | Migrate to a fixed release |
| 7.9 | 7.9.2 or 7.9.21, each with SMU CSCwn39554 |
| 7.10 | 7.10.2 with SMU CSCwn39554 |
| 7.11 | 7.11.2 or 7.11.21, each with SMU CSCwn39554 |
| 24.1 | 24.1.2 with SMU CSCwn39554 |
| 24.2 | 24.2.2 with SMU, or 24.2.21 |
| 24.3 | 24.3.2 with SMU CSCwn39554 |
| 24.4 | 24.4.2 |
| 25.1 and later | Not affected |
Cisco notes the patches are "In-Service Software Upgrade (ISSU)/Reload SMU install impact type", so plan a window.
The stopgap filter
There is no workaround, but there is a mitigation: "filter UDP traffic that is destined to the infrastructure address space with UDP destination port 1701." Cisco suggests doing it with an infrastructure access list on edge interfaces, to "drop UDP port 1701 traffic that is destined for local router addresses while continuing to forward transit traffic." Cisco's usual caution applies: test it in your own network first. To check whether a card has already reset, Cisco gives "show logging | include "NP.*reset"". Cisco says it "is not aware of any public announcements or malicious use" of this flaw.
The eMudhra certificate notice
Cisco's eMudhra informational, last updated 2026 November 4, covers certificate authorities whose keys were broken; Cisco says anyone holding them "can issue fraudulent TLS/HTTPS certificates for any domain on the internet." IOS XR Software is on the list of impacted products with software fixes, with Cisco's IOS XR guidance page and a target of "26.4.1 (Nov 30, 2026)". If your routers rely on public certificates, read the IOS XR guidance now and put that release in your plan.
Buying an ASR 9000 or its parts
If you are buying, check two things before you order: which line cards will go in, and which IOS XR release the router will run. A chassis whose line cards are all outside Cisco's lists is outside this advisory; a router with the named cards needs a fixed release or the filter above before it goes live.
We have an ASR 9000 chassis, a second chassis option, and route switch processors such as this RSP and an older RSP in stock. Everything is on the ASR 9000 shelf, with other routers under routers.
When you ask for a quote, name the line cards and release you plan to run. For how this router sits beside Cisco's other routers and firewalls, see our Cisco router and firewall guide and the Cisco guide.